Cloud Security
Stop Overprivileged Cloud Identities Before They Leak Data
Overprivileged identities hide in plain sight, granting silent access to resources they never touch until an attacker exploits the gap.
Overprivileged identities hide in plain sight, granting silent access to resources they never touch until an attacker exploits the gap.
Authority overrides scrutiny, allowing attackers to manipulate payment processes without technical exploits.
Default macro blocking stops most automated infections but breaks legacy workflows, forcing a shift toward application-level trust rather than user discretion.
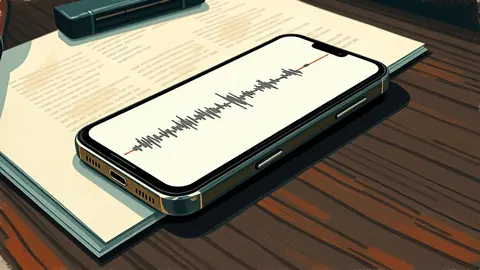
Synthetic audio often lacks natural breathing and exhibits unnaturally flat emotional resonance that human speech rarely maintains under stress.
Attackers use voice calls to bypass email filters, forcing staff to validate fraud through direct human interaction rather than digital analysis.
Most financial damage occurs in the first hour. You must isolate the compromised account before any funds leave the organisation, as speed outweighs perfect forensic detail.
Entitlements define the exact actions an identity can perform, yet most teams grant broad access that creates invisible attack surfaces within the cloud environment.
Multi-factor authentication stops credential theft but introduces latency that can disrupt automated infrastructure management pipelines.
The physical distance between an attacker and your system determines the baseline severity of every vulnerability you track.
Changing session identifiers after login fails if the application reuses the same token for authenticated and unauthenticated states in the same request cycle.
NoSQL injection often bypasses standard WAF rules because the payload is structural data rather than executable code, requiring a distinct containment strategy.
Synthetic media relies on statistical probability rather than visual perfection, meaning detection often fails when the generation parameters are unknown.
Small organisations often host cryptocurrency mining software on their own servers, turning legitimate hardware into unauthorised computational assets for attackers.
Physical paper remains a persistent attack vector because digital security controls rarely extend to the final output of office equipment.
Simulating a breach exposes communication gaps that technical controls cannot fix, saving money by preventing operational paralysis during a real incident.
Transparency requires tracing every input and output stage, revealing where proprietary opacity hides systemic bias and data leakage risks.
Most intrusions persist for months because defenders monitor for known signatures rather than analysing behavioural anomalies across the environment.
Cloud penetration testing reveals how attackers exploit permission boundaries rather than just firewalls, exposing gaps in identity management that traditional scans miss.
Determine whether your data volume and latency constraints require shallow algorithms or deep neural networks for your security operations.
Detect subtle infrastructure anomalies and silent API calls that indicate compromised credentials before data exfiltration completes.